Secure the Coding Agent. Secure the Software it Creates.
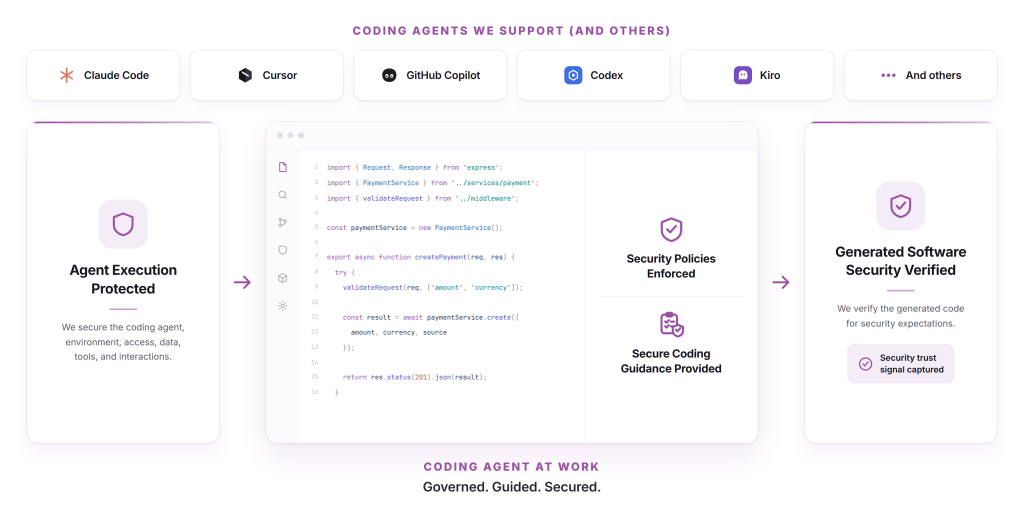
Paradigm protects coding-agent interactions, sensitive data, and tool execution, guides software creation with secure coding requirements, and independently verifies generated software for vulnerabilities. CodeChain connects this security evidence to a continuous trust record that evolves with the software.
Secure
Protect the coding agent throughout execution.
Verify
Independently verify the software for vulnerabilities.
Trust
Security verification becomes a trust signal for the software.
Prompt Injection
Jailbreak Attacks
Sensitive Data Exposure
Unauthorized Tool Usage
Hallucinations & Unsafe Outputs
Unsafe Agent Actions
Shadow AI
Secrets & Credential Leakage
Prompt Injection
Jailbreak Attacks
Sensitive Data Exposure
Unauthorized Tool Usage
Hallucinations & Unsafe Outputs
Unsafe Agent Actions
Shadow AI
Secrets & Credential Leakage
Execution Flow
Protect the Coding Workflow. Verify the Software.
Apply security controls to coding-agent requests, access, and actions. Guide software creation with enterprise security requirements, then independently verify the result and connect the evidence to continuous trust through CodeChain.

Protect Prompts
Detect prompt injection, jailbreaks, and unsafe requests before they reach approved models.
Request blocked

Secure Execution
Check coding-agent actions and tool calls against enterprise security policies before execution.
Policies enforced

Control Access
Allow coding agents to use approved models according to identity and permissions.
Access enforced

Protect Data
Detect sensitive data, secrets, and credentials. Block or redact exposure during coding.
Content protected

Guide Coding
Apply secure coding guidance and enterprise security requirements as agents create software.
Guidance applied

Verify Software
Independently verify security and intent alignment. Record the resulting evidence in CodeChain.
Evidence recorded
Security Capabilities
Secure Coding Agents. Generate Trusted Software.
Protect coding activity, guide secure software creation, and independently verify the result. Connect security evidence to continuous trust through CodeChain.
Secure your coding interactions.
Understand developer intent and evaluate coding-agent prompts to detect harmful instructions before they reach models, tools, or enterprise systems.
Identify prompt intent and classify security risks.
Block prompt injection, jailbreaks, malicious content, and unsafe coding instructions.
10:21:12 Prompt received from dev. coding agent
10:21:14 Intent identified: code generation
10:21:15 Violation: PROMPT_INJECT_BLOCK enforced
10:21:16 Request blocked due to high-risk prompt
10:21:17 No access to model, tools, data, or systems
No access to model, tools, data, or systems
10:24:03 Tool call requested: read_file
10:24:10 Policy check: Allowed
10:24:16 MCP request: github.create_branch
10:24:19 Policy check: Allowed
10:24:21 Action Executed
Secure Coding Agent Execution
Control coding-agent actions before execution to protect development systems and enforce enterprise security policies.
Inspect and authorize tool calls, MCP requests, commands, and API calls.
Enforce least privilege and block risky or unauthorized actions.
Protect Enterprise Data and Credentials
Protect sensitive enterprise information during coding-agent interactions and software generation.
Detect and block exposure of API keys, credentials, secrets, and personally identifiable information.
Redact or mask sensitive content according to enterprise data protection policies.
10:28:01 Detected: AWS Access Key ID in prompt
10:28:11 Detected: Email address in prompt
10:28:27 Action taken: both values redacted (policy applied)
10:28:31 Prompt forwarded to model with redacted values
10:28:21 Response returned without sensitive data
09:18:03 Task analyzed: implement user authentication
09:18:04 Enterprise security policies identified and applied
09:18:06 Relevant OWASP ASVS Authentication (V6) guidance applied
09:18:07 Relevant OWASP Top 10 guidance identified and applied
09:18:09 Secure coding guidance sent to agent
Guide Secure Software Creation
Provide coding agents with enterprise security requirements and secure coding guidance during generation, helping developers create software aligned with enterprise standards.
Apply relevant guidance from OWASP ASVS and OWASP Top 10.
Incorporate enterprise security policies, approved skills, and development requirements into software creation.
Independently Verify Generated Software
Independently evaluate generated software before it is returned to the developer, checking its alignment with developer intent and secure coding requirements.
Identify vulnerabilities and deviations from enterprise security requirements.
Return findings to the developer or trigger remediation according to enterprise policy.
Connect verification evidence to CodeChain to support continuous trust as the software evolves.
09:20:13 Generated code received
09:20:11 Intent alignment check: passed
09:20:14 Vulnerability detected: Input validation issue (CWE-20)
09:20:16 Remediation policy: Auto-fix permitted
09:20:17 Fix applied automatically
09:20:19 Security trust signal captured
READY TO GET STARTED?
See Secure AI Development in Action.
Discover how Paradigm protects coding-agent execution, guides secure software creation, and independently verifies the result. See how CodeChain connects security evidence to continuous trust in the software your developers create.